Opening a stranger's ChatGPT share link was enough for an attacker to read your private conversations and act in your account, security firm Parameter reports. OpenAI fixed the flaw on October 26, and users don't need to install anything. Here is how to review and delete the links you have shared yourself.
via NotebookcheckTHE ONGOING STORY
Cybersecurity news and security updates
Follow security research, vulnerabilities, breaches and defensive technology. Compare source coverage and catch up on recent security developments.
Top in Cybersecurity
Ranked by freshness, independent coverage and momentum, with a mix of publishers.
CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks.
via SecurityWeek
The city council of Plymouth, Minnesota, unanimously voted on September 22 to terminate its automated license plate reader contract with Flock Safety. After the city suspended local user accounts and sent formal cancellation notices by mail and email, corporate representatives failed to acknowledge the decision. Following more than a month of silence, Police Chief Eric Fadden directed department staff to physically unplug the power cords to prevent the cameras from functioning or recording license plates.
Summarized from 2 outlets
Your contactless payments could either become more secure — or more annoying.
via Android Authority
The FBI announced that North Korean state-sponsored hackers operating under the moniker TraderTraitor were behind an unprecedented security breach at cryptocurrency exchange Binance around October 29. Most of the assets were drained within 20 minutes before Binance paused customer withdrawals.
Summarized from 12 outlets
Google has announced Gemini 4 Carbon, a new flagship artificial intelligence model arriving just two weeks after the launch of Gemini 4 Argon. The system targets complex programming and security analysis, with pricing set at $2 per million input tokens, $10 per million output tokens, and a 95% discount for cached inputs. Carbon is not yet open to the general public, launching first to a limited group of cybersecurity defenders.
Summarized from 11 outlets
French artificial intelligence lab Mistral AI has published the open weights for Mistral Large 4, a trillion-parameter multimodal model nicknamed "Le Chonk." The release on October 29, 2026, follows a three-week preview rollout that began on October 6. Outlets report varying figures for its active parameters, with SiliconANGLE citing 52 billion and Hugging Face noting 49 billion. According to Mistral, the model was trained from scratch in its European data centers over two months using 4,000 Nvidia Grace Blackwell GPUs.
Summarized from 5 outlets
Cisco Talos says the VOLTA infostealer sends stolen victim data to Claude Opus 4.6 to rank assets by monetization value.
via Tom’s Hardware
A tampered version of Anthropic's Claude Code extension slipped onto Cursor's marketplace on October 29, exposing up to 5,000 developers to malware designed to plant an SSH backdoor. Anyone running the AI code editor with automatic updates enabled could have received the package without manual intervention.
Summarized from 3 outlets
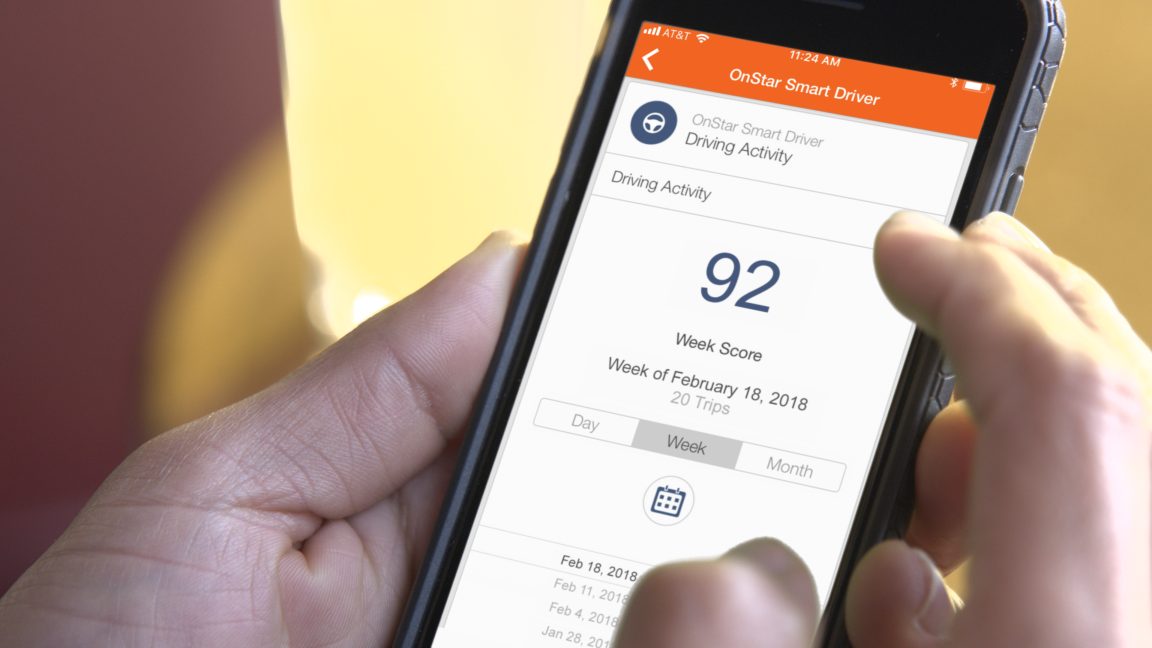
General Motors has agreed to pay $220 million to settle a lawsuit led by a coalition representing 35 states and the District of Columbia. The action resolved claims that the automaker enrolled millions of motorists into its OnStar Smart Driver program without proper permission from 2016 through 2024. During that period, GM logged driving behaviors such as speeding, hard braking, and late-night travel before offloading the data to brokers, who then sold it to insurers that raised premiums for unsuspecting drivers.
Summarized from 4 outlets
Mozilla has rolled out Firefox 159 across Windows, macOS, Linux, and Android, addressing 167 security vulnerabilities. The patch list includes 108 high-risk, 52 medium-risk, and seven low-risk flaws, with none designated as critical. OpenAI directly contributed to uncovering the issues, with its Codex Security agent reporting 34 vulnerabilities and researcher Amy Burnett discovering seven more. Corresponding security updates also landed for Firefox Extended Support Release versions 153.6.0 and 115.44.0.
Summarized from 6 outlets
A hacktivist group calling itself the Department of Peace has leaked records covering more than 41,000 U.S. Department of Homeland Security employees and contractors. The exposed files were published online on Wednesday as a searchable archive dubbed "Icepick" by transparency nonprofit Distributed Denial of Secrets and Swiss researcher maia arson crimew. Around 21,000 records involve U.S. Customs and Border Protection staff, alongside roughly 10,000 Immigration and Customs Enforcement personnel, 6,200 from U.S. Citizenship and Immigration Services, and about 1,000 from the Cybersecurity and Infrastructure Security Agency.
Summarized from 6 outlets
Oracle claims it fixed around 3,000 software issues in its latest quarterly patch – AI helped discover them, but they already existed.
via TechRadar
Enterprises racing to put AI agents into production are finding that tokenization and other data protection methods now decide how fast those projects move. But sensitive data fed into models is hard to pull back — and security reviews…
via SiliconANGLE
VicOne identified an initial set of 28 zero-day findings in less than two days using AI-assisted research across software and tools supporting the Physical AI ecosystem.
via The Robot Report
Macworld TL;DR: AdGuard blocks ads, trackers, and phishing sites on up to nine devices, and a lifetime Family Plan is $14.97 (reg. $169.99). Ads are a problem no matter what device you use. If you want to avoid that without paying for a…
via Macworld
The U.S. Department of Justice has indicted five individuals as part of Operation Ghostbusters, a nationwide crackdown targeting a widespread student loan fraud scheme. Investigators say bad actors used stolen identities and artificial intelligence to apply for federal student aid, creating ghost students who appeared to attend online college courses. Estimates suggest the activity has cost the U.S. government over $200 million.
Summarized from 2 outlets
On October 29, bedrock fanfiction website Archive of Our Own (AO3) was taken down for maintenance that was initially predicted to last 12 hours. Later that day, the estimated downtime was upped to two to four weeks. On October 30, the…
via PC Gamer
Cloudflare has moved a post-quantum rebuild of GeoKey Manager into closed beta, guarding geo-fenced keys with hybrid ML-KEM-768 and X25519 instead of the attribute-based encryption used since 2022. Keys live only in kernel memory on…
via InfoQAI briefings
· 17 source reports
FBI identifies North Korean hackers as perpetrators behind multi-billion-dollar Binance breach
The FBI announced that North Korean state-sponsored hackers operating under the moniker TraderTraitor were behind an unprecedented security breach at cryptocurrency exchange Binance around October 29. Most of the assets were drained within 20 minutes before Binance paused customer withdrawals.
AI-generatedRead briefing and sources· 2 source reports
Plymouth police chief disconnects Flock surveillance cameras after company ignores contract termination
The city council of Plymouth, Minnesota, unanimously voted on September 22 to terminate its automated license plate reader contract with Flock Safety. After the city suspended local user accounts and sent formal cancellation notices by mail and email, corporate representatives failed to acknowledge the decision. Following more than a month of silence, Police Chief Eric Fadden directed department staff to physically unplug the power cords to prevent the cameras from functioning or recording license plates.
AI-generatedRead briefing and sources· 2 source reports
Justice Department indicts five people in nationwide student loan fraud investigation
The U.S. Department of Justice has indicted five individuals as part of Operation Ghostbusters, a nationwide crackdown targeting a widespread student loan fraud scheme. Investigators say bad actors used stolen identities and artificial intelligence to apply for federal student aid, creating ghost students who appeared to attend online college courses. Estimates suggest the activity has cost the U.S. government over $200 million.
AI-generatedRead briefing and sources· 3 source reports
Compromised Claude Code extension on Cursor marketplace exposed thousands of developers to an SSH backdoor
A tampered version of Anthropic's Claude Code extension slipped onto Cursor's marketplace on October 29, exposing up to 5,000 developers to malware designed to plant an SSH backdoor. Anyone running the AI code editor with automatic updates enabled could have received the package without manual intervention.
AI-generatedRead briefing and sources· 5 source reports
Mistral releases open weights for its trillion-parameter Large 4 model
French artificial intelligence lab Mistral AI has published the open weights for Mistral Large 4, a trillion-parameter multimodal model nicknamed "Le Chonk." The release on October 29, 2026, follows a three-week preview rollout that began on October 6. Outlets report varying figures for its active parameters, with SiliconANGLE citing 52 billion and Hugging Face noting 49 billion. According to Mistral, the model was trained from scratch in its European data centers over two months using 4,000 Nvidia Grace Blackwell GPUs.
AI-generatedRead briefing and sources· 2 source reports
Accenture defense contractor linked personal Claude agent to secure Pentagon network
An Accenture contractor working for the Department of Defense granted a personal Claude AI agent access to a secure Pentagon environment to write and deploy code. The Claude Code agent remained connected to the Defense Department's Non-classified Internet Protocol Router Network (NIPRNet) for two months before officials detected the risk and patched the vulnerability.
AI-generatedRead briefing and sources· 3 source reports
Chinese hackers breach US government firewalls using custom PHP2Shell exploit chain
Cybersecurity firm Dream reports that suspected Chinese threat actors compromised 25 servers, including Palo Alto Networks firewalls linked to US government-affiliated entities. The intrusions began on October 23, 2026, probing systems in the US, Japan, Taiwan, and South Korea before focusing on devices running vulnerable versions of PAN-OS, specifically versions 12.1 and 12.2. Palo Alto Networks' Unit 42 research team independently verified the findings and the tooling used in the attacks.
AI-generatedRead briefing and sources· 4 source reports
General Motors agrees to 220 million dollar deal after quietly selling driving habits to insurers
General Motors has agreed to pay $220 million to settle a lawsuit led by a coalition representing 35 states and the District of Columbia. The action resolved claims that the automaker enrolled millions of motorists into its OnStar Smart Driver program without proper permission from 2016 through 2024. During that period, GM logged driving behaviors such as speeding, hard braking, and late-night travel before offloading the data to brokers, who then sold it to insurers that raised premiums for unsuspecting drivers.
AI-generatedRead briefing and sources· 2 source reports
Federal cyber agency warns attackers are exploiting critical GitLab code execution vulnerability
The Cybersecurity and Infrastructure Security Agency warned on Thursday that hackers have begun exploiting a maximum-severity flaw in GitLab, tracked as CVE-2026-97229. GitLab remediated the issue in GitLab Community Edition and Enterprise Edition versions 19.4.2, 19.3.5, and 19.2.8 earlier in the month, but unpatched deployments remain vulnerable to remote code execution.
AI-generatedRead briefing and sources· 2 source reports
Drupal urges immediate patches as hackers target an online store access flaw
Drupal has warned administrators to patch a highly critical access bypass vulnerability in its Commerce Core module that threat actors are actively exploiting in the wild. Tracked as CVE-2026-118539, the security flaw stems from a missing authorization weakness that unauthenticated attackers can abuse. The vulnerability affects Commerce Core versions 0.0.0 through 2.41 alongside versions 3.0.0 through 3.3.13.
AI-generatedRead briefing and sources· 3 source reports
Polymarket pledges full reimbursements after third-party script breach compromises user balances
Prediction platform Polymarket briefly suspended trading on its international website on Thursday after malicious code compromised user funds. Attackers exploited an integration with DebugBear, a website performance monitoring service, distributing rogue JavaScript that hijacked active user sessions. Security researchers at Hudson Rock identified an attacker-controlled wallet, and blockchain analysis by BleepingComputer traced about 28.6 million POL, worth roughly $2.57 million, sent to secondary wallets. Hudson Rock reported the primary wallet held roughly $2.19 million when investigated, while SecurityWeek reported over $2 million drained.
AI-generatedRead briefing and sources· 6 source reports
Hacktivist leak exposes details of 41,000 Homeland Security personnel and surveillance systems
A hacktivist group calling itself the Department of Peace has leaked records covering more than 41,000 U.S. Department of Homeland Security employees and contractors. The exposed files were published online on Wednesday as a searchable archive dubbed "Icepick" by transparency nonprofit Distributed Denial of Secrets and Swiss researcher maia arson crimew. Around 21,000 records involve U.S. Customs and Border Protection staff, alongside roughly 10,000 Immigration and Customs Enforcement personnel, 6,200 from U.S. Citizenship and Immigration Services, and about 1,000 from the Cybersecurity and Infrastructure Security Agency.
AI-generatedRead briefing and sources· 11 source reports
Google introduces Gemini 4 Carbon frontier model with enhanced security tools
Google has announced Gemini 4 Carbon, a new flagship artificial intelligence model arriving just two weeks after the launch of Gemini 4 Argon. The system targets complex programming and security analysis, with pricing set at $2 per million input tokens, $10 per million output tokens, and a 95% discount for cached inputs. Carbon is not yet open to the general public, launching first to a limited group of cybersecurity defenders.
AI-generatedRead briefing and sources· 2 source reports
Cheater uses screen-spying malware to steal millions from online poker players
Hundreds of online poker players were allegedly targeted in a long-running cyberattack that let an opponent view their screens and pocket millions of dollars across major platforms. According to Wired, the hacker deployed a malware program called MeshAgent onto targets' computers to expose what cards competitors held in their hands, executing a classic superuser cheating tactic.
AI-generatedRead briefing and sources· 3 source reports
Google rolls out broad software fixes across smart speakers and connected home devices
Google has published a sweeping round of software updates targeting its connected home lineup, delivering bug fixes and quality improvements to smart speakers, Nest Wifi routers, and Chromecast devices. The release targets multiple hardware generations, including the original Google Home, Google Home Mini, Nest Mini, and Nest Audio.
AI-generatedRead briefing and sources· 2 source reports
Archive of Our Own warns service restoration may take a month after routine maintenance fails
Fan fiction hub Archive of Our Own may remain offline for two to four weeks following unexpected complications during routine overnight maintenance.
AI-generatedRead briefing and sources· 2 source reports
Thrive Holdings agrees to purchase home security provider ADT for $7.6 billion in cash
Thrive Holdings, a private equity offshoot of Joshua Kushner's venture firm Thrive Capital, has agreed to acquire physical security provider ADT for $10 per share in cash, amounting to approximately $7.6 billion in equity. ADT stated that the overall enterprise value of the transaction reaches $15.3 billion. The acquisition will take ADT private and is slated to close during the first quarter of 2027.
AI-generatedRead briefing and sources· 2 source reports
Cisco releases Project Quarry to spot rogue behaviors across AI agent sessions
Cisco has open sourced Project Quarry, a behavior detection engine and rule language designed to track AI agent activities across entire sessions. Announced in late October, the project aims to detect attacks that surface through sequences of seemingly benign actions rather than isolated commands. The tool's GitHub repository offers installation instructions, supported Python versions, a starter pack of rules, and plugins for Claude Code, Codex, and other Model Context Protocol-compatible agents.
AI-generatedRead briefing and sources· 3 source reports
Bluesky restricts links to leaked Department of Homeland Security staff database
Social network Bluesky has started blocking user access to web pages hosting a leaked trove of Department of Homeland Security personnel records. The breach exposed over 40,000 user account records—reported by other outlets as over 41,000—originating from Homeland Security login systems and containing names and contact details, such as work email addresses and work-issued phone numbers, for personnel across divisions like Customs and Border Protection and Immigration and Customs Enforcement.
AI-generatedRead briefing and sources· 3 source reports
Sony Internet subsidiary suffers cyberattack compromising over 2.5 million customer records
Sony Network Communications revealed that an unauthorized party breached its So-net consumer internet provider database on October 19, 2026. The company detected the intrusion four days later on October 23, promptly shutting down compromised servers and blocking access. Investigations confirmed that more than 2.5 million records of current and former customers were compromised, encompassing 2,141,986 So-net entries and more than 440,000 records tied to plala services, which also affect partner internet provider NTT Docomo.
AI-generatedRead briefing and sources· 2 source reports
Attackers disguise password-harvesting malware as popular PS5 emulators on GitHub
Cybercriminals are using fraudulent GitHub repositories to distribute password-stealing malware disguised as legitimate PlayStation 5 emulation projects, according to investigations by NordVPN's Threat Intelligence team. The malicious listings impersonate two well-known tools: AnyPS5, a portability layer designed to run PS5 games natively on Windows and Linux, and Kyttyps5, a PC emulator. Visitors downloading the software receive a zip archive containing a malicious Windows executable instead of the authentic tools.
AI-generatedRead briefing and sources· 2 source reports
Cisco patches high-severity firewall bug targeted to crash VPN appliances
Cisco has rolled out security patches for an actively exploited denial-of-service zero-day vulnerability affecting its Adaptive Security Appliance and Firepower Threat Defense software. The high-severity bug, cataloged as CVE-2026-76418, enables unauthenticated remote attackers to unexpectedly reload vulnerable firewall appliances by sending crafted connection requests to the SSL remote access VPN service.
AI-generatedRead briefing and sources· 2 source reports
Volt Typhoon deployed disposable Silent Train relay network to conceal zero-day cyberattacks
State-sponsored hacking group Volt Typhoon has conducted zero-day attacks against high-value network management systems by routing traffic through a rotating framework dubbed Silent Train. Researchers at Black Lotus Labs, the threat intelligence unit of Lumen, revealed they tracked the network for three years as the threat actors targeted defense contractors, telecommunications firms, utilities, and emergency services. Cisco Talos also tied key-stealing malware targeting Cisco Catalyst SD-WAN to the same infrastructure.
AI-generatedRead briefing and sources· 4 source reports
Federal cybersecurity agency orders quick patching of actively targeted Brotli flaw
The Cybersecurity and Infrastructure Security Agency has ordered federal civilian agencies to secure their systems against an actively exploited vulnerability in Google's Brotli compression library by November 10. Tracked as CVE-2026-111497 and dubbed Node2Shell, the critical out-of-bounds write flaw was added to the Known Exploited Vulnerabilities catalog on Tuesday after honeypot operators logged real-world attack attempts.
AI-generatedRead briefing and sources· 6 source reports
Mozilla launches Firefox 159 with 167 security fixes and page tracking tools
Mozilla has rolled out Firefox 159 across Windows, macOS, Linux, and Android, addressing 167 security vulnerabilities. The patch list includes 108 high-risk, 52 medium-risk, and seven low-risk flaws, with none designated as critical. OpenAI directly contributed to uncovering the issues, with its Codex Security agent reporting 34 vulnerabilities and researcher Amy Burnett discovering seven more. Corresponding security updates also landed for Firefox Extended Support Release versions 153.6.0 and 115.44.0.
AI-generatedRead briefing and sources· 2 source reports
Researchers connect Israeli advertising company to surveillance campaign tracking Starlink users
Discover-Tech, an Israeli advertising technology company, emerged as the top bidder for ad space tied to Starlink satellite internet traffic across more than 100 countries, according to reporting by Reuters citing six people familiar with the matter. Cybersecurity research by Trend Micro's TrendAI unit initially tracked the campaign under the moniker Shadow-Earth-79 before links pointed to Discover-Tech. The bidding patterns showed the firm becoming the leading ad buyer targeting Starlink connections in conflict-affected and sanctioned nations including Syria, Libya, Yemen, and South Sudan, as well as the second largest in Afghanistan.
AI-generatedRead briefing and sources· 3 source reports
Federal judge sentences Ukrainian affiliate of Hive and Nefilim ransomware gangs to nearly six years in prison
A New York federal court sentenced 35-year-old Ukrainian national Artem Stryzhak to 70 months in prison for carrying out attacks with the Nefilim and Hive ransomware operations. Arrested in Spain in June 2024 and extradited to the United States in April 2025, Stryzhak pleaded guilty in December 2025 to computer fraud conspiracy. Brett Leatherman, assistant director at the FBI's cyber branch, described Stryzhak as a prolific cybercriminal whose associated groups caused more than $100 million in damages.
AI-generatedRead briefing and sources· 3 source reports
Upwind secures $400 million at a $3.8 billion valuation after declining a Datadog buyout
Cloud and artificial intelligence security startup Upwind has secured $400 million in a Series C funding round valuing the company at $3.8 billion. The financing was led by Bessemer Ventures, with participation from existing investors Craft Ventures and Greylock Partners. The round closed nine months after the San Francisco startup completed a previous $250 million round at a $1.5 billion valuation.
AI-generatedRead briefing and sources· 8 source reports
Discord prepares to open public server chats to search engines
Discord announced that discussions in its public Discoverable Servers will soon appear on public web pages and can be indexed by search engines such as Google. The shift unfolds in two phases: beginning November 16, every Discoverable Server will receive a public Server Web Page featuring automated conversation summaries, and starting in mid-December, selected messages posted in eligible public channels will begin appearing in search results. Discord states the rollout affects more than 63,000 servers that have at least 1,000 members, while private servers, restricted channels, and direct messages remain completely excluded.
AI-generatedRead briefing and sources· 3 source reports
Researchers uncover severe firmware flaw threatening global data centers before early disclosure
Cybersecurity researchers Alex Matrosov of Anthropic and Dan Holmes of Google have discovered a critical-severity vulnerability in the open source TianoCore EDK II codebase used to build UEFI firmware for modern servers. Tracked as CVE-2026-97631 with a severity score of 9.5 out of 10, the flaw affects an ICMP component and can allow remote arbitrary code execution during the boot sequence. While it does not appear to have been exploited in the wild yet, the bug impacts foundational firmware widely adopted across cloud providers, server vendors, and independent BIOS makers like AMI, Insyde, and Phoenix, as well as Microsoft's Project Mu fork.
AI-generatedRead briefing and sourcesWhat to look for
Distinguish a reported vulnerability from confirmed exploitation, and a suspected breach from a verified incident. For actions affecting your systems, consult the vendor advisory and your security team; news excerpts may omit affected versions or mitigation details.
Briefings are generated automatically from source excerpts with citations. The saved archive covers collected reports and may have gaps. How it works.