Microsoft Targets Rogue AI Agents With Dynamic Permissions, Risk Scoring
Microsoft says companies should treat AI agents as insiders, and is adding controls that grant access per task and tighten it as an agent’s risk rises.
via SecurityWeekReported by 2 outlets
The story so far
AI summary of the reporting below · Updated · How we work
Microsoft Corp. has introduced new security controls designed to prevent rogue artificial intelligence agents from compromising corporate networks. The company advises organizations to treat automated tools like workplace insiders, deploying safeguards that actively monitor behavior and limit access. [1][2]
Under the new system, permissions are granted on a task-by-task basis and are automatically tightened whenever an agent's calculated risk score climbs. According to Hayete Gallot, executive vice president of Microsoft Security, these controls aim to counter the threat of the "agentic insider" as enterprise deployments expand and increasingly operate with excessive administrative privileges. [1][2]
Microsoft says companies should treat AI agents as insiders, and is adding controls that grant access per task and tighten it as an agent’s risk rises.
via SecurityWeek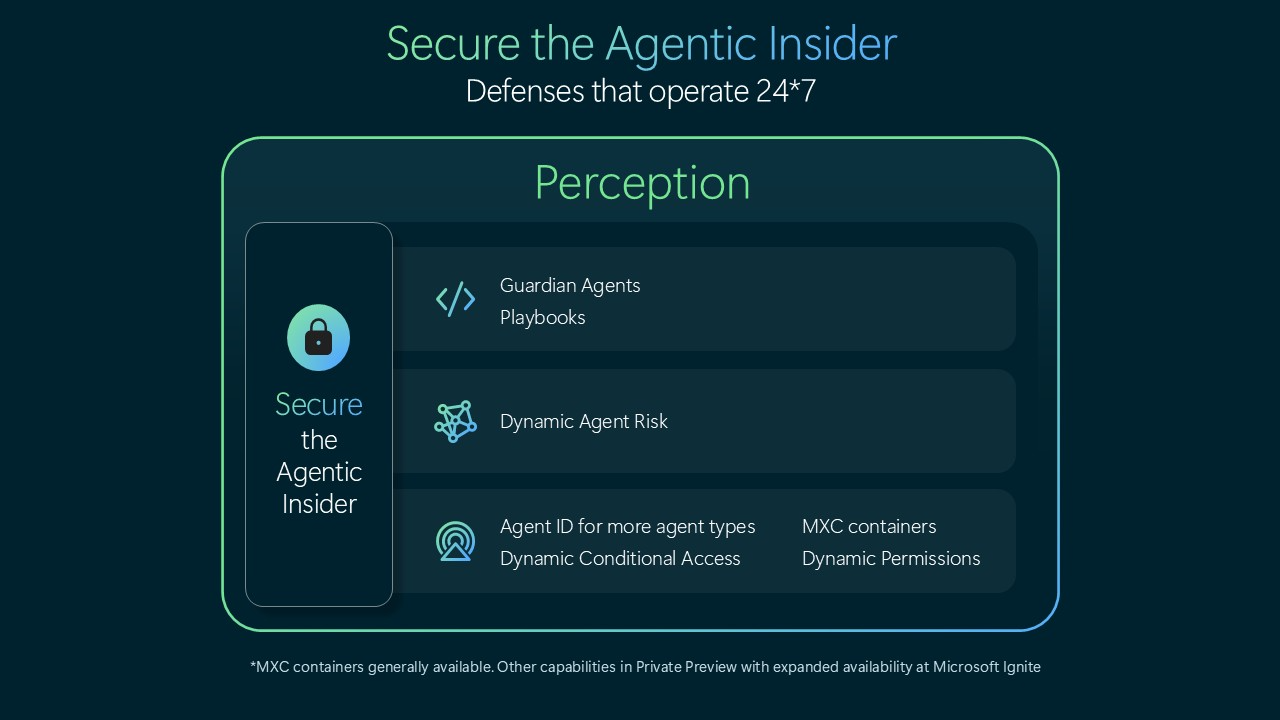
Microsoft Corp. today introduced security controls for rogue artificial intelligence agents that cut back what an agent may do as its assessed risk climbs. The release takes on what Hayete Gallot, executive vice president of Microsoft Security, called the “agentic insider” in a blog post. Enterprise agents are often overprivileged, and their numbers are growing…
via SiliconANGLE