Fortinet warns of critical FortiMail flaw exploited in zero-day attacks
Source summary · The RegisterNo login required, exploitation underway, and some admins are still waiting for patches
3 reporting groups · Read the storyGathering the saved reports for your topic and time period.
See what happened while you were away.
Sep 27, 2026 – Oct 4, 2026 · Rolling 7 days · UTC
From our saved archive, collecting since Oct 4, 2026. This covers reports we captured, not every event. The selected period starts before collection began; earlier coverage is limited to reports captured later. How catch-ups work
No login required, exploitation underway, and some admins are still waiting for patches
3 reporting groups · Read the story
The AdGuard Family Plan lifetime subscription, which normally costs $169.99, is available for $11 until October 4. The plan protects up to nine devices from advertisements and tracking elements. [1][2]
2 reporting groups · Read the story
Amid the rapid rise in AI agents requesting “Full Disk Access” to your Mac, Apple says it is making changes to macOS to protect user privacy. While the company hasn’t shared specifics, Apple says users should understand what it means to give an app such “extraordinary” access to their Mac.
2 reporting groups · Read the story
The China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by exploiting SharePoint vulnerabilities to gain initial access.
2 reporting groups · Read the story
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI.
2 reporting groups · Read the story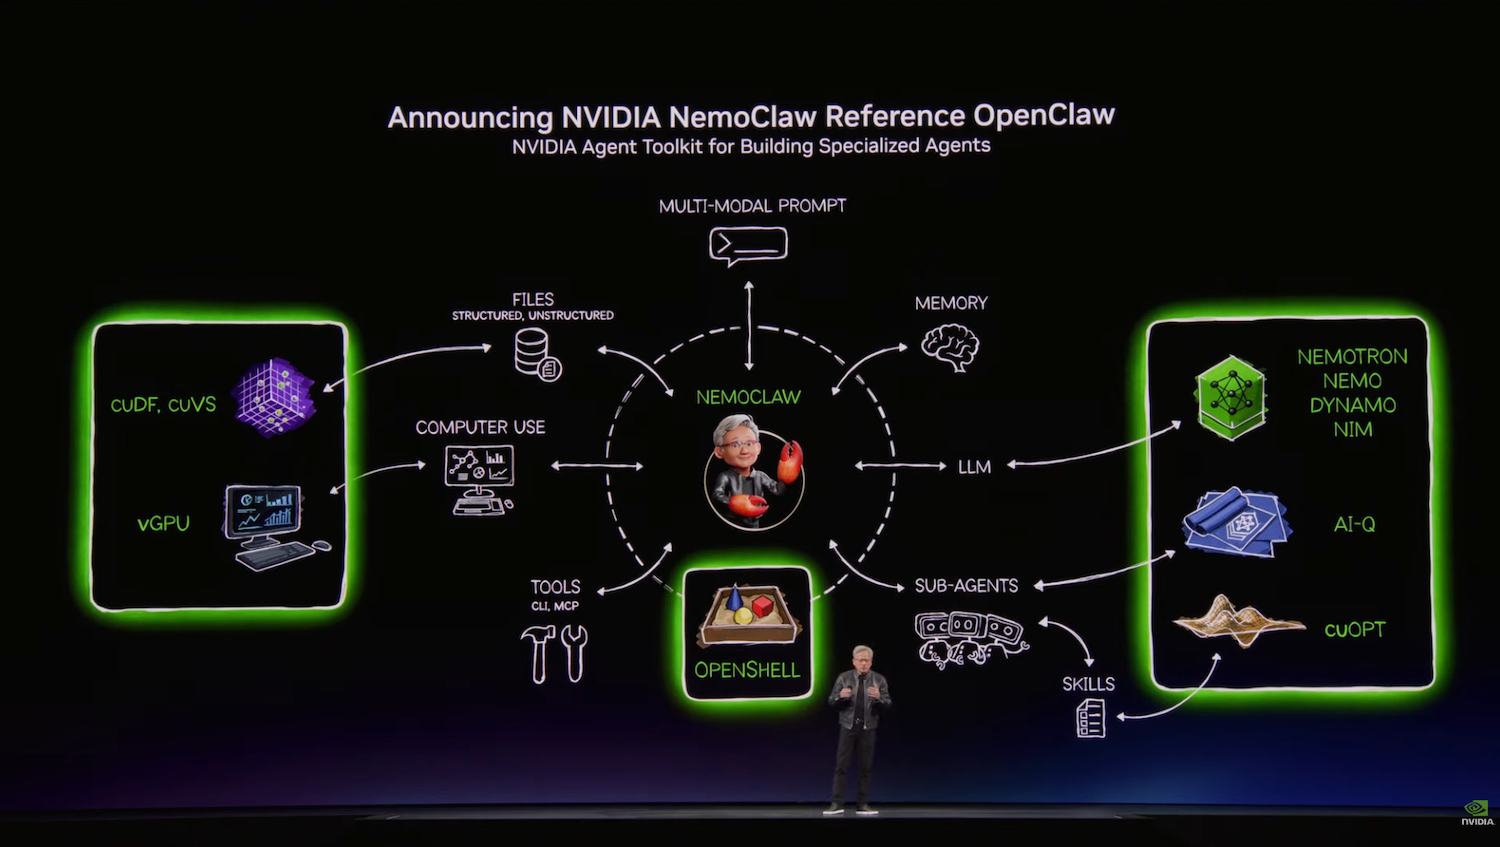
NVIDIA is taking on agentic AI security with the new Open Agent Safety Platform and OpenShell 0.1.0 frameworks
2 reporting groups · Read the storyHere’s some exciting news for those using a UniFi Network Video Recorder (UNVR) from Ubiquiti: The company today announced the release candidate of UniFi Protect 7.3 with major improvements that, among other things, ease the pain of storage costs. The official 7.3 version is set to come out as soon...
GitLab warned customers today to immediately patch a critical AI Gateway vulnerability that could let attackers run arbitrary commands on vulnerable instances.
From snooping smart glasses to AI bots going rogue, I’m not surprised US adults are more concerned about their privacy.
Mostly 'routine research tasks,' and 'some involved government websites, which our models often use,' AI giant tells The Reg
Save $129 on Arlo’s 2025 4K HDR 2-camera bundle with SmartHub, now at a record low for sharp wireless home security.
Amid the rapid rise in AI agents requesting “Full Disk Access” to your Mac, Apple says it is making changes to macOS to protect user privacy. While the company hasn’t shared specifics, Apple says users should understand what it means to give an app such “extraordinary” access to their Mac.
This authentic-looking scam starts with a sponsored Google link – and it’s catching people off-guard.
TL;DR Google is testing biometric authentication before password autofill in Chrome for Android. The feature has returned in Chrome Canary after Google previously tested and pulled a similar implementation before stable release. The flag works for some users, but it didn’t trigger on a Pixel 8 in testing, suggesting the rollout is still limited or incomplete. Google Chrome on Android does a lot of heavy lifting when it comes to passwords.
Frontline Education is notifying school districts of a data breach after attackers exploited a vulnerability in third-party software to gain unauthorized access to its systems and steal employee information, including Social Security numbers.
DHS agents not only tracked and intimidated people observing ICE activity in Maine, but stored information about them in a Palantir-built database, newly unsealed court filings say.
AI-native cybersecurity requires defenses that can keep pace with attackers while protecting infrastructure that never stops running. That challenge is bringing security expertise and specialized computing closer together, with automation embedded throughout the systems enterprises use to train and run models. CrowdStrike’s fastest observed eCrime attacker breakout time in 2025 was 27 seconds, underscoring the…
Instead of a watchable video stream, you’ll get text descriptions or alerts about detected people, pets or activity.
Meta says FDA isn't sufficient to Muse reading messages. Apple begs to differ.
The proposed legislation would extend to all automotica license plate readers.
A recent article by Anil Madhavapeddy argues that AI agents can turn publicly available clues about software vulnerabilities into working exploits, reducing the effectiveness of traditional disclosure embargoes in open source projects. The author highlights the need for faster patching and release processes as the time between vulnerability disclosure and exploitation shrinks. By Renato Losio
California state Attorney General Rob Bonta issued a subpoena to OpenAI, compelling it to submit information on the hacking incidents that its models have been involved in. While the investigators haven't determined yet whether the company has broken any rules or regulations, Bonta said that developers are responsible for the models they build and should be held legally accountable if they perpetrate cyberattacks.
The bugs could lead to authentication bypass, shell command execution, and memory corruption.
doxx.net’s new ADN platform prevents agentic misadventure while the agent is operating under the user’s authority.
Google suspends product vulnerability submissions to its Open Source Software Vulnerability Reward Program (OSS VRP) over an influx of invalid AI-driven reports.
Millions have downloaded Meta’s AI agent Muse. But getting it to do your bidding comes with privacy costs.
Until routers on Asus’s 3.0.0.6_102 firmware are updated, the company says not to import untrusted VPN files.
The Technical University of Denmark (DTU) says information belonging to up to 200,000 users may have been exposed after hackers accessed its identity and access management system and downloaded a large amount of data.
Ahead of Newegg's Fantastech Sale II launch on October 5th, you can grab some early deals and have price protection security if the product price drops lower in the sale proper.
Exploitation attempts came from China-hosted IP, VulnCheck researcher says
CVE-2026-85706 is a critical GitLab path-traversal vulnerability that has moved beyond theoretical risk into confirmed exploitation. It affects self-managed GitLab CE/EE and could allow an unauthenticated remote attacker to read arbitrary files from the GitLab. By Sergio De Simone