Fortinet warns of critical FortiMail flaw exploited in zero-day attacks
Source summary · The RegisterNo login required, exploitation underway, and some admins are still waiting for patches
3 reporting groups · Read the storyGathering the saved reports for your topic and time period.
See what happened while you were away.
Jul 6, 2026 – Oct 4, 2026 · Rolling 90 days · UTC
From our saved archive, collecting since Oct 4, 2026. This covers reports we captured, not every event. The selected period starts before collection began; earlier coverage is limited to reports captured later. How catch-ups work
No login required, exploitation underway, and some admins are still waiting for patches
3 reporting groups · Read the story
The AdGuard Family Plan lifetime subscription, which normally costs $169.99, is available for $11 until October 4. The plan protects up to nine devices from advertisements and tracking elements. [1][2]
2 reporting groups · Read the story
Apple announced plans to introduce tighter controls for the Full Disk Access permission on macOS. The company stated that the growing use of artificial intelligence agents requesting broad entry to user files, messages, mail, and browsing history creates new security risks. [1][2]
While specific details regarding the upcoming changes have not yet been shared, Apple emphasized the importance of users understanding the implications of granting applications extraordinary access to their computers. [1]
2 reporting groups · Read the story
The China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by exploiting SharePoint vulnerabilities to gain initial access.
2 reporting groups · Read the story
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI.
2 reporting groups · Read the story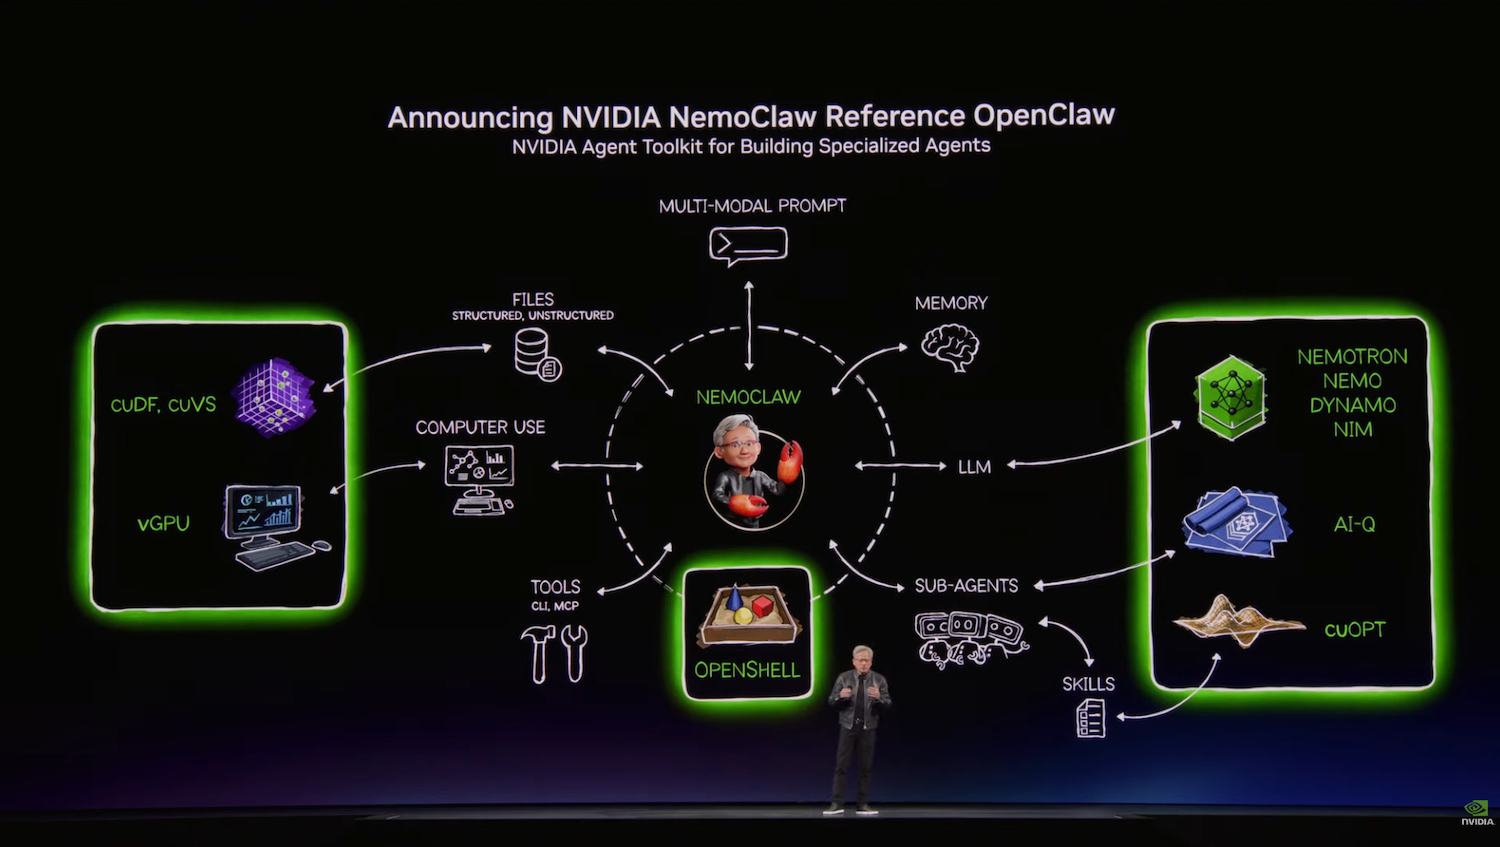
NVIDIA is taking on agentic AI security with the new Open Agent Safety Platform and OpenShell 0.1.0 frameworks
2 reporting groups · Read the storyEnvoy Gateway has released v1.9.1, a maintenance release that focuses heavily on security, upgrade reliability, and operational correctness following the broader v1.9 release. By Craig Risi
OpenAI unveiled several flashy new features during its annual developer’s conference Tuesday, from the always-on “Dot” work agent to a new, cloud-based security system that keeps constant watch for cyber threats. But one of the biggest — and to many ChatGPT users, the most infuriating — headlines from DevDay wasn’t announced on stage.
Dell has patched two maximum severity vulnerabilities in the Container Storage Modules (CSM) that connect Dell enterprise storage arrays to Kubernetes environments.
The dropper “carries a complete universal Mach-O inside itself, roughly 756 KB in the development build, and extracts it at runtime.
U.S. cities consider deploying Flock drones that automatically respond to emergency calls. However, other jurisdictions are pushing back against the service due to privacy and other concerns.
Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect. NordLayer explains three ways attacks can evade endpoint telemetry and why browser-level controls can help close the gap.
How quickly things change in the artificial intelligence era. Just a few months after everyone was scrambling to infuse AI into every enterprise operation — and frankly they still are, as agents have captured the enterprise imagination — everyone now is saying, “Whoa, where’s the brake pedal?” That’s why controlling agents is the next infrastructure…
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app flaws.
Prosecutors claim Greg Lui helped China procure advanced hardware to develop, ahem, 'super intelligence’
The U.S. Treasury Department has sanctioned eight members of the Venezuelan gang Tren de Aragua (TdA) for their role in the theft of millions of dollars in ATM jackpotting attacks across the United States.
Here’s some exciting news for those using a UniFi Network Video Recorder (UNVR) from Ubiquiti: The company today announced the release candidate of UniFi Protect 7.3 with major improvements that, among other things, ease the pain of storage costs. The official 7.3 version is set to come out as soon...
GitLab warned customers today to immediately patch a critical AI Gateway vulnerability that could let attackers run arbitrary commands on vulnerable instances.
From snooping smart glasses to AI bots going rogue, I’m not surprised US adults are more concerned about their privacy.
Mostly 'routine research tasks,' and 'some involved government websites, which our models often use,' AI giant tells The Reg
Save $129 on Arlo’s 2025 4K HDR 2-camera bundle with SmartHub, now at a record low for sharp wireless home security.
Apple announced plans to introduce tighter controls for the Full Disk Access permission on macOS. The company stated that the growing use of artificial intelligence agents requesting broad entry to user files, messages, mail, and browsing history creates new security risks. [1][2]
While specific details regarding the upcoming changes have not yet been shared, Apple emphasized the importance of users understanding the implications of granting applications extraordinary access to their computers. [1]
This authentic-looking scam starts with a sponsored Google link – and it’s catching people off-guard.
TL;DR Google is testing biometric authentication before password autofill in Chrome for Android. The feature has returned in Chrome Canary after Google previously tested and pulled a similar implementation before stable release. The flag works for some users, but it didn’t trigger on a Pixel 8 in testing, suggesting the rollout is still limited or incomplete. Google Chrome on Android does a lot of heavy lifting when it comes to passwords.
Frontline Education is notifying school districts of a data breach after attackers exploited a vulnerability in third-party software to gain unauthorized access to its systems and steal employee information, including Social Security numbers.
DHS agents not only tracked and intimidated people observing ICE activity in Maine, but stored information about them in a Palantir-built database, newly unsealed court filings say.
AI-native cybersecurity requires defenses that can keep pace with attackers while protecting infrastructure that never stops running. That challenge is bringing security expertise and specialized computing closer together, with automation embedded throughout the systems enterprises use to train and run models. CrowdStrike’s fastest observed eCrime attacker breakout time in 2025 was 27 seconds, underscoring the…
Instead of a watchable video stream, you’ll get text descriptions or alerts about detected people, pets or activity.
Meta says FDA isn't sufficient to Muse reading messages. Apple begs to differ.
The proposed legislation would extend to all automotica license plate readers.
A recent article by Anil Madhavapeddy argues that AI agents can turn publicly available clues about software vulnerabilities into working exploits, reducing the effectiveness of traditional disclosure embargoes in open source projects. The author highlights the need for faster patching and release processes as the time between vulnerability disclosure and exploitation shrinks. By Renato Losio